S3 access for non-technical teams: the complete guide
Everything a company needs to give finance, operations, legal and media staff safe access to files in Amazon S3, without AWS Console logins, in reading order.
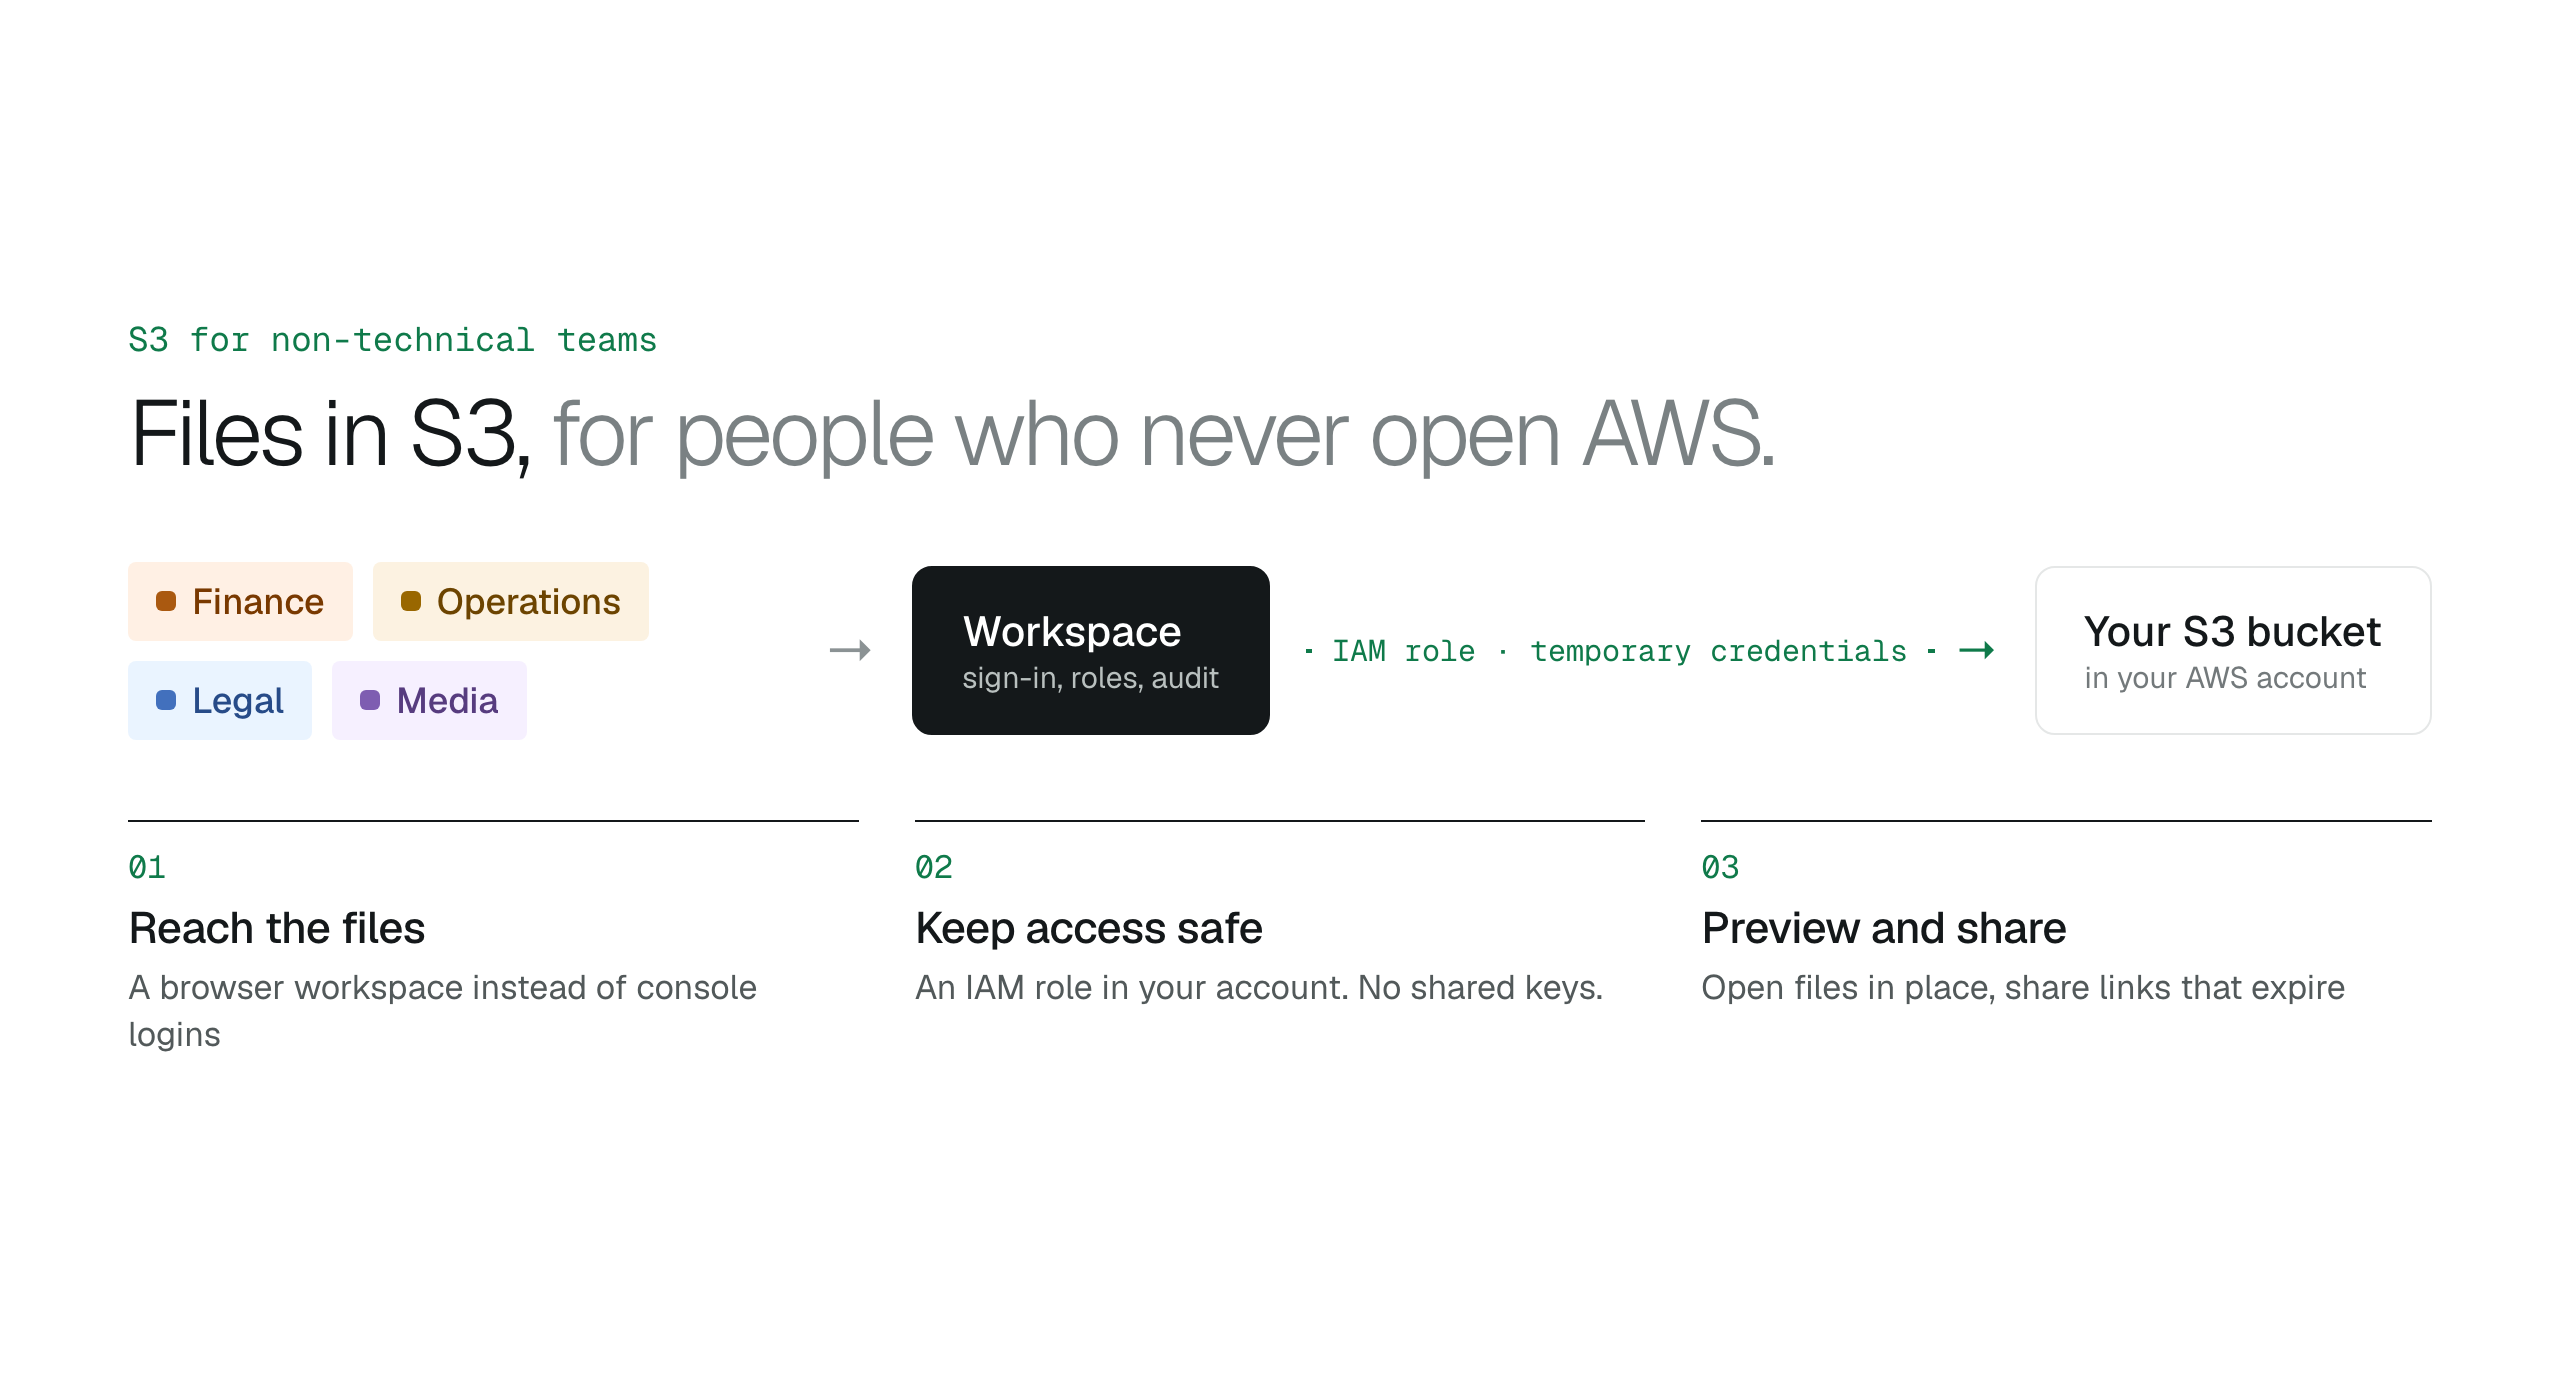
Keep files in S3, give tools a scoped IAM role instead of keys, and pick the access layer by who needs the files: one link for one file, a component for an app you build, a workspace for teams who need previews, sharing and roles.
Many companies keep contracts, invoices, scans and media in Amazon S3 because it is cheap, durable and already inside their AWS account. The engineers are happy. Everyone else has to ask them for files, or gets an AWS Console login they were never meant to have.
This guide collects our articles on that problem in the order most teams meet it: first the ways people can reach files at all, then how to keep access safe, then what people need once they can see the files, and finally how to choose a tool.
Start here: the ways people can reach S3 files
There are four common answers: a presigned link for one file, an AWS-managed web portal, the Storage Browser component inside an app you build, and a workspace with sign-in and roles. Each fits a different job. The first article compares all four; the second describes what a good business-facing workspace looks like.
How to access Amazon S3 files without the AWS consoleThe best way to manage business files in Amazon S3How to create S3 presigned URLs for downloads and uploads
Once people can see the files: previews and sharing
Access alone is not enough if every PDF, spreadsheet or iPhone photo has to be downloaded to be opened, or if sharing a file with a client still means a script. Previews in the browser and share links that expire and can be revoked are what make S3 usable day to day. Some teams also want to ask questions about a document; choosing a Bedrock model for document Q&A explains the trade-offs.
How to preview files in Amazon S3 without downloading themChoosing a browser-based S3 file viewer for business documentsSecure file sharing for business: what to check before you send the linkHow to see inside a zip file in Amazon S3 without downloading it
Choosing a tool
Desktop clients such as Cyberduck, S3 Browser and Transmit suit people comfortable with credentials. AWS's Storage Browser suits teams building their own app. A shared S3 workspace like BucketDesk suits companies where many non-technical people need the same files with roles and an audit trail. These comparisons are honest about when each one wins.
When Storage Browser for Amazon S3 is the better choiceCyberduck, S3 Browser or Transmit? Choosing an S3 file browser for a business teamA security checklist before a whole team gets S3 accessPlans, seats and what each one includesChoosing document management software when the files are in your own cloud storage
Read the white paper
Primary sources
Discussion
0 comments · open to guests · moderatedLiked this? Get the next article by email. No schedule, no digest, one click to leave.