How do presigned URLs work? S3 downloads, uploads and expiry
What an S3 presigned URL is and how it works, how to create one with the AWS CLI, boto3 and the JavaScript SDK, the credential rule that makes them expire early, presigned POST for browser uploads, and what each error actually means.
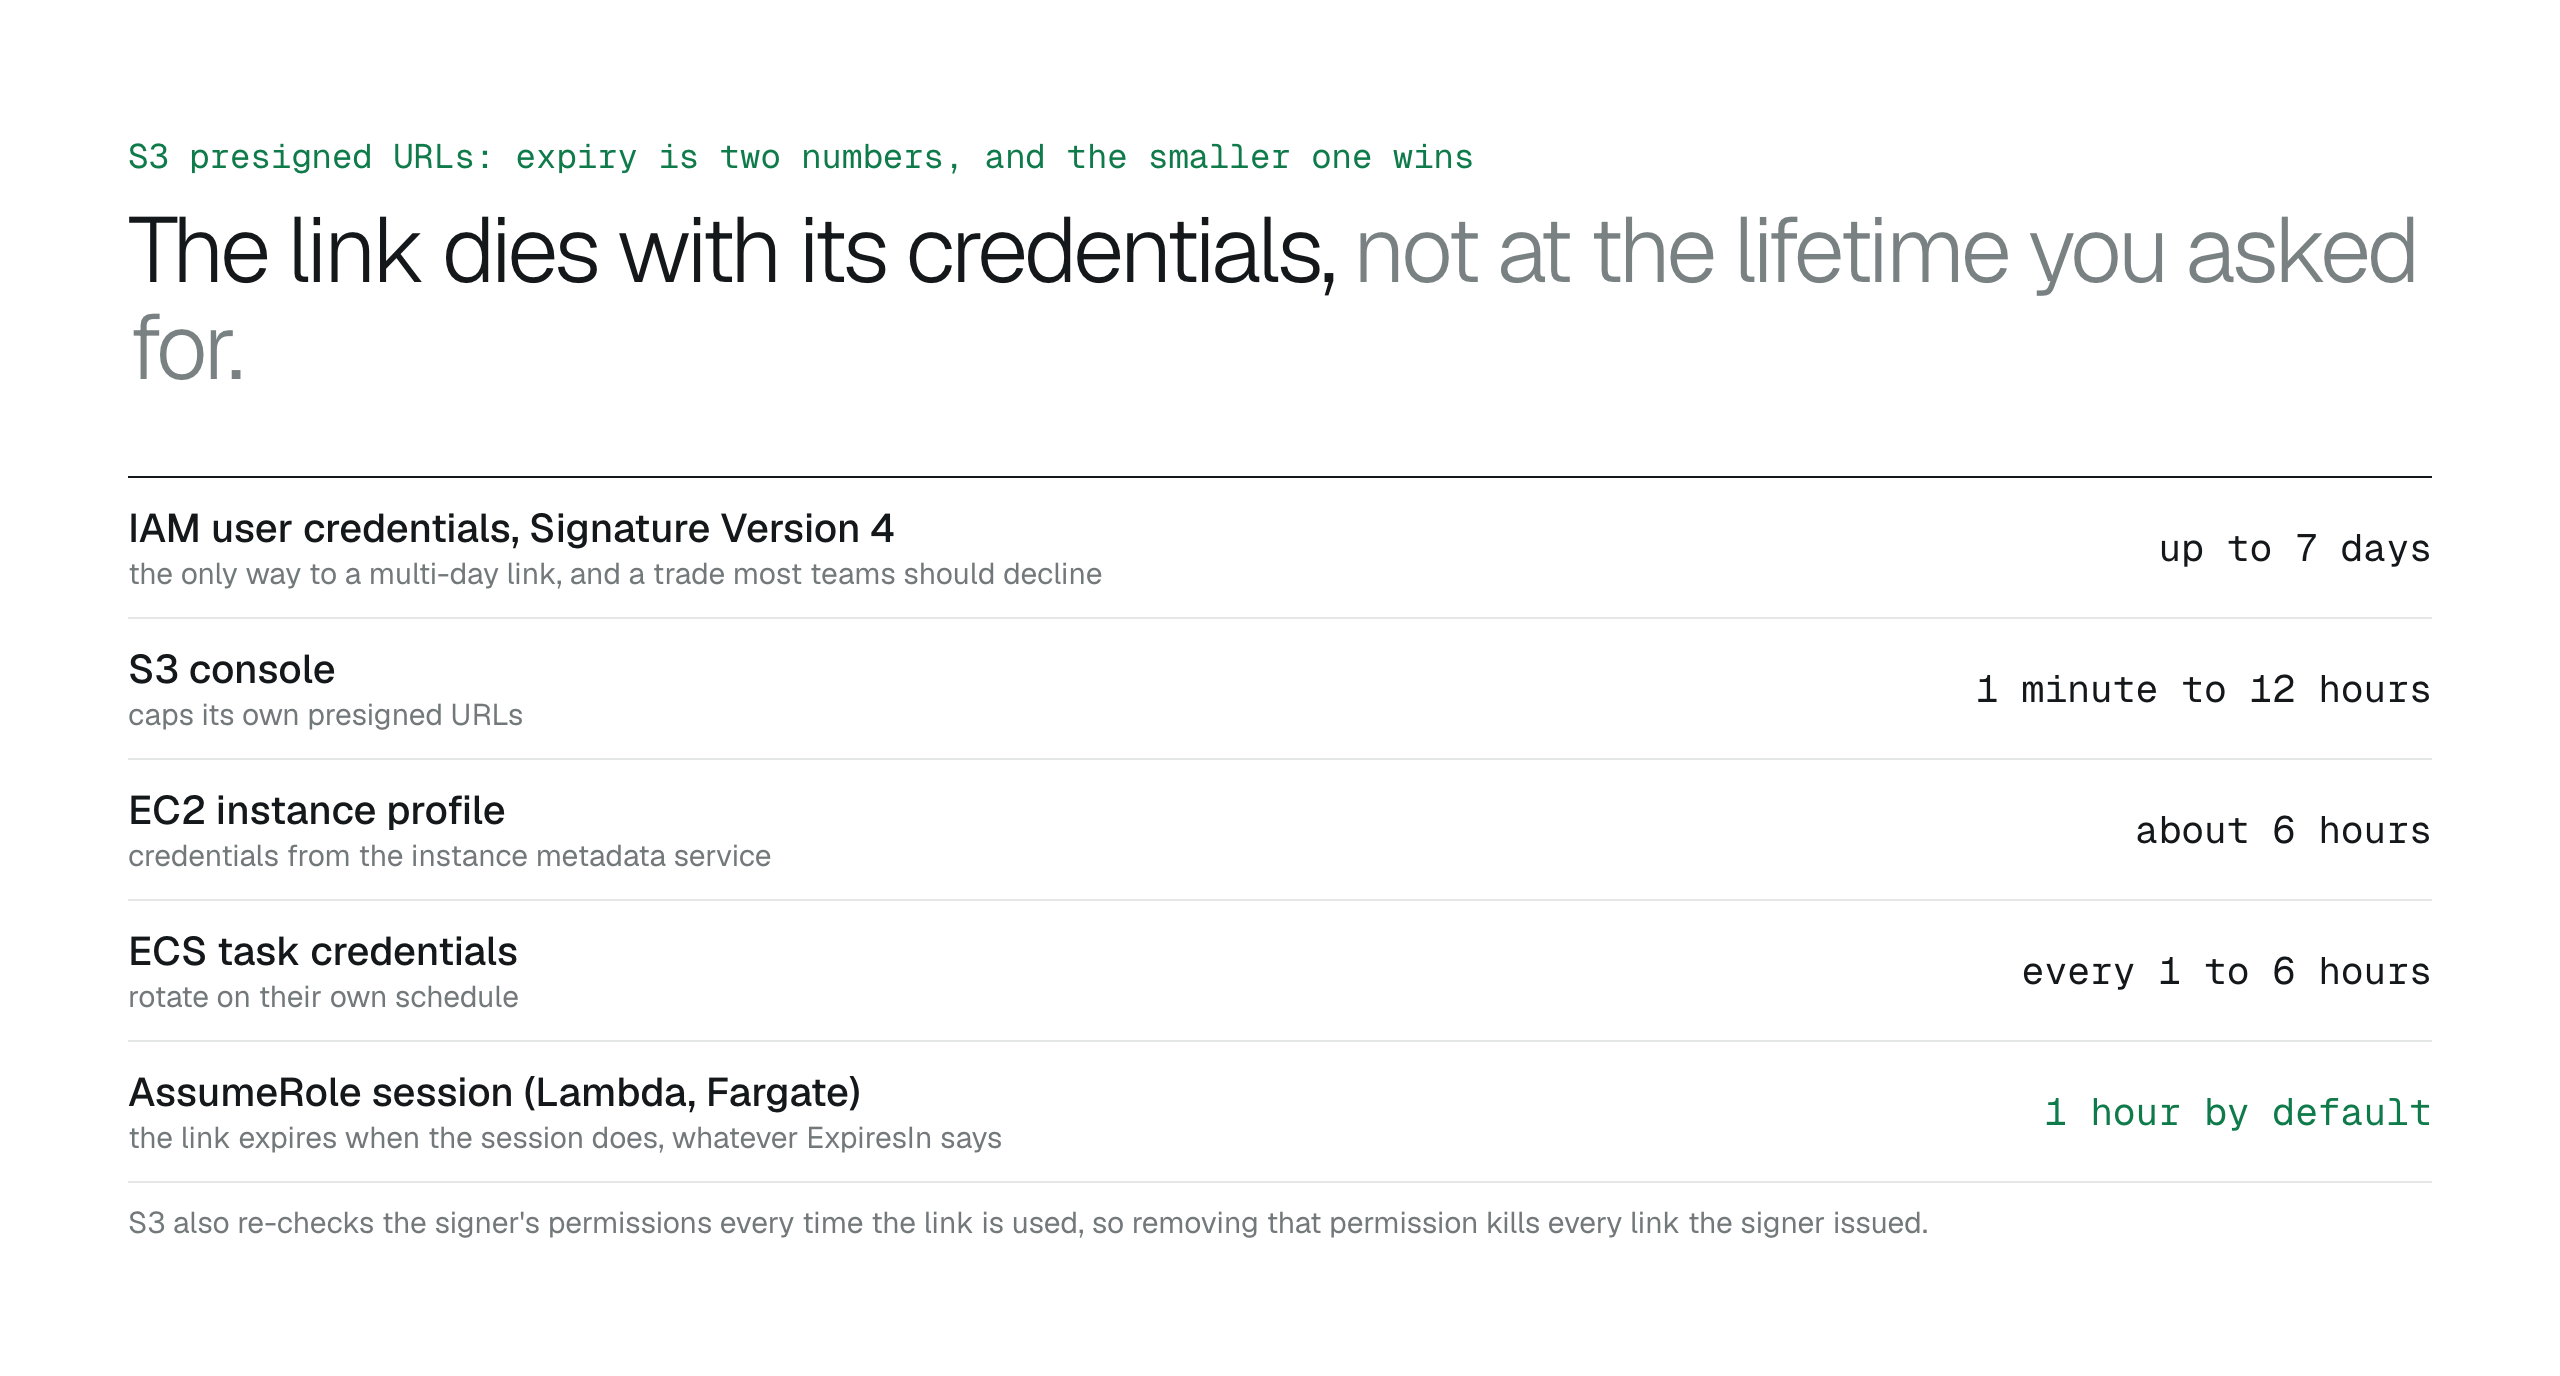
An S3 presigned URL is a SigV4-signed request that anyone can use until it expires, and S3 checks the signer's permissions every time. Sign with the narrowest role that can do the job, and assume the URL will expire with that role's session rather than at the lifetime you asked for. Use a presigned PUT for a trusted uploader and a presigned POST with content-length-range for an untrusted one. Cap the whole bucket with s3:signatureAge if links are part of your workflow, and when the requirement includes revocation, recipient identity or a record of who opened what, use something other than a presigned URL.
An S3 presigned URL is a signed request that grants temporary access to a specific object and operation. A recipient can use the link without an AWS account, but the request still depends on the signer’s permissions and applicable AWS policies.
A download link is permission to retrieve the specified object. An upload link authorizes a write to the specified key. Neither link gives the recipient general access to browse your bucket.
What is a presigned URL?
It is an ordinary S3 request with the authentication moved into the query string. The URL carries the permissions of the IAM principal who created it, so the recipient can do exactly what that principal could do to that object, and nothing more. Anyone with valid credentials can create one, but it only works if the signer had permission for the operation being signed.
You choose four things when you create it: the bucket, the object key, the HTTP method (GET to download, PUT to upload, HEAD to read metadata) and an expiration interval. The URL can be used more than once until it expires, which is worth saying out loud, because "single use" is a common and wrong assumption. If you presign a PUT for a key that already exists, the upload replaces the existing object.
Treat the URL as a bearer token. AWS says so directly: possession is the whole authorisation. Anything that copies a URL, such as a forwarded email, a chat log, a proxy access log or a browser history sync, hands over the access with it.
How do presigned URLs work?
Creating a presigned URL makes no call to AWS. Your SDK or the CLI takes the request you describe, signs it locally with Signature Version 4 using your secret key, and appends the result to the object's normal address as query parameters.
X-Amz-Algorithm names the signing method. X-Amz-Credential identifies the access key and the date, Region and service the signature is scoped to. X-Amz-Date is when it was signed and X-Amz-Expires is how many seconds it stays valid after that. X-Amz-SignedHeaders lists the headers that were part of the signature, and X-Amz-Signature is the signature itself. Temporary credentials add X-Amz-Security-Token.
When the link is used, S3 recomputes the signature from the request it actually received and compares it with X-Amz-Signature. Any difference in the method, key, query string or a signed header means the request is rejected. S3 then checks that the signature has not expired, that the signing credentials are still valid, and that the principal behind them still has permission for the operation at that moment. The last check is the important one: permission is evaluated when the URL is used, not when it was created.
https://amzn-s3-demo-bucket.s3.us-east-1.amazonaws.com/contracts/acme-msa.pdf
  ?X-Amz-Algorithm=AWS4-HMAC-SHA256
  &X-Amz-Credential=AKIAIOSFODNN7EXAMPLE%2F20261013%2Fus-east-1%2Fs3%2Faws4_request
  &X-Amz-Date=20261013T090000Z
  &X-Amz-Expires=900
  &X-Amz-SignedHeaders=host
  &X-Amz-Signature=<64 hex characters>
Expiry is two numbers, and the smaller one wins
The lifetime you request is a ceiling, not a promise. The URL also dies when the credentials that signed it stop being valid, and for anything running on AWS those credentials are usually temporary.
Signed with IAM user credentials under Signature Version 4, a presigned URL can be valid for up to 7 days, which is 604,800 seconds. Signed with a role session, it expires when the session does, even if you asked for longer. An AssumeRole session defaults to one hour. EC2 instance profile credentials from the instance metadata service have a maximum validity of roughly 6 hours. ECS task credentials typically rotate every one to six hours. The S3 console caps its own presigned URLs between 1 minute and 12 hours.
This is the single most reported surprise with presigned URLs, and it has a plain consequence: a Lambda function or a Fargate task cannot mint a link that outlives its own role session, no matter what ExpiresIn says. If you genuinely need a multi-day link, you need long-lived credentials to sign it with, which is a trade most teams should decline rather than engineer around.
S3 checks the expiry when the HTTP request starts. A large download that began just before expiry keeps going; if the connection drops and the client retries afterwards, it fails.
Create a presigned URL with the AWS CLI
The AWS CLI has aws s3 presign, which signs a GET and nothing else, so it only makes download links. Its default expiry is 3,600 seconds, and --expires-in takes a value in seconds up to 604,800, the 7-day maximum. Presigned URLs use Signature Version 4, so set the bucket's Region explicitly with --region or in your profile. For uploads, use an SDK.
# Download link valid for 15 minutes. GET only; default is 3600 seconds.
aws s3 presign s3://amzn-s3-demo-bucket/contracts/acme-msa.pdf \
  --expires-in 900 --region us-east-1
Create a presigned URL in Python with boto3
In boto3, generate_presigned_url signs any client method, so the same call makes download and upload links. The useful extra is that you can override the response headers for that one request, which is how a PDF stored with a generic content type is made to open in the browser tab instead of downloading, without modifying the object.
For an upload, put ContentType in Params. It becomes part of the signature, and the uploader must send exactly that Content-Type header or S3 answers SignatureDoesNotMatch.
import boto3

s3 = boto3.client("s3", region_name="us-east-1")

# Download: GET, valid for 15 minutes.
url = s3.generate_presigned_url(
    "get_object",
    Params={
        "Bucket": "amzn-s3-demo-bucket",
        "Key": "contracts/2026/acme-msa",
        # Override the stored headers for this response only.
        "ResponseContentType": "application/pdf",
        "ResponseContentDisposition": "inline",
    },
    ExpiresIn=900,
)

# Upload: one key, one recipient, replaces the object if it exists.
put_url = s3.generate_presigned_url(
    "put_object",
    Params={
        "Bucket": "amzn-s3-demo-bucket",
        "Key": "inbox/signed-contract.pdf",
        "ContentType": "application/pdf",
    },
    ExpiresIn=900,
)

# The uploader then runs:
# curl -X PUT -T signed-contract.pdf -H "Content-Type: application/pdf" "$PUT_URL"Create a presigned URL in JavaScript (AWS SDK v3)
In the JavaScript SDK v3, the signer lives in a separate package, @aws-sdk/s3-request-presigner. Its getSignedUrl function takes the S3 client and a command object, so GetObjectCommand gives you a download link and PutObjectCommand an upload link. expiresIn is in seconds and defaults to 900 when you leave it out.
import { S3Client, GetObjectCommand, PutObjectCommand } from "@aws-sdk/client-s3";
import { getSignedUrl } from "@aws-sdk/s3-request-presigner";

const client = new S3Client({ region: "us-east-1" });

// Download link, valid for 15 minutes.
const getUrl = await getSignedUrl(
  client,
  new GetObjectCommand({ Bucket: "amzn-s3-demo-bucket", Key: "contracts/acme-msa.pdf" }),
  { expiresIn: 900 },
);

// Upload link. ContentType is signed, so the upload must send the same header.
const putUrl = await getSignedUrl(
  client,
  new PutObjectCommand({
    Bucket: "amzn-s3-demo-bucket",
    Key: "inbox/signed-contract.pdf",
    ContentType: "application/pdf",
  }),
  { expiresIn: 900 },
);

// In the browser or another service:
await fetch(putUrl, { method: "PUT", headers: { "Content-Type": "application/pdf" }, body: file });
Uploads: presigned PUT or presigned POST
A presigned PUT URL is the simple case. The recipient sends the file body to the URL and it becomes the object. You control the key, because you signed it, and you can pin the content type by signing it too. What you cannot control is size: nothing stops someone sending a 40 GB file to a URL you meant for a signed contract.
A presigned POST is the browser-form case, and it is the one to reach for when the uploader is untrusted. Instead of a bare URL you generate a URL plus a set of form fields containing a signed policy, and that policy can carry conditions. content-length-range caps the file size before a byte is accepted. starts-with on the key lets the client choose a filename inside a prefix you control. In boto3 it is generate_presigned_post.
Under Signature Version 4 you can also require a checksum on upload, such as CRC-32, CRC-32C, CRC-64/NVME, SHA-1 or SHA-256, by signing the corresponding header, which turns a silent corruption into a rejected request. Large files that arrive this way often go on to background jobs; how BucketDesk unpacks big ZIP archives on AWS Batch covers that side.
post = s3.generate_presigned_post(
    "amzn-s3-demo-bucket",
    "inbox/${filename}",
    Fields={"Content-Type": "application/pdf"},
    Conditions=[
        {"Content-Type": "application/pdf"},
        ["starts-with", "$key", "inbox/"],
        # Reject anything outside 1 KB to 25 MB before it is accepted.
        ["content-length-range", 1024, 26214400],
    ],
    ExpiresIn=900,
)

# post["url"] is the form action; post["fields"] are hidden inputs,
# and the file input must come last in the form.
Limiting what the holder can do
Because the URL inherits the signer's permissions, the first control is to sign with a role that has only the permission you intend to delegate. A presigned URL created by an administrator is an administrator's access to that object.
Beyond that, three bucket-side controls are worth knowing. The s3:signatureAge condition, measured in milliseconds, denies requests whose signature is older than a given age, which caps every presigned URL against the bucket regardless of what lifetime the signer asked for. The s3:authType condition lets you deny presigned requests outright: presigned URLs arrive as REST-QUERY-STRING and presigned POSTs as POST, while normal SDK calls use REST-HEADER. Denying REST-QUERY-STRING also stops uploads and downloads in the S3 console, so plan an exception for console users. And a network-path restriction using aws:SourceIp, aws:SourceVpc or aws:SourceVpce requires requests to arrive from your network, which applies to presigned URLs along with everything else.
None of these revokes a single link. Because S3 checks the signer's permissions when the URL is used, you can kill outstanding links by removing that permission from the signing role, deactivating the access key that signed them, or deleting the object. Each of those affects every link the same signer issued, not just the one you meant.
{
  "Sid": "DenyPresignedOlderThan10Minutes",
  "Effect": "Deny",
  "Principal": "*",
  "Action": "s3:*",
  "Resource": "arn:aws:s3:::amzn-s3-demo-bucket/*",
  "Condition": { "NumericGreaterThan": { "s3:signatureAge": "600000" } }
}The errors, and what each one means
- 403 Forbidden: the signing principal lacked the permission for that operation, or a bucket policy explicitly denies it. Check the signer's permissions before you check the URL.
- ExpiredToken: the temporary credentials used to sign have expired. The URL cannot outlive them; refresh the credentials and sign again.
- SignatureDoesNotMatch on upload: the Content-Type header sent with the PUT differs from the one that was signed. Send exactly the signed value, or sign without one.
- SignatureDoesNotMatch in general: clock drift on the signing host, a corporate proxy rewriting headers or query strings, a URL edited or unquoted in a shell, or a client configured for a different Region than the bucket.
- AccessDenied with HeadersNotSigned: if-range: when Range is in the signed headers, S3 requires If-Range to be signed too if it is present in the request.
- The URL works for you and not for the recipient: you are testing while signed in to the console. Try it in a private window, which is the only honest test.
S3 presigned URL vs CloudFront signed URL
Both are links with an expiry, but they are signed by different things and checked in different places. An S3 presigned URL is signed with IAM credentials and checked by S3, so it inherits the IAM limits above: at most 7 days, shorter with a role session, and dead when the signer loses permission.
A CloudFront signed URL is signed with a private key whose public key you register in a trusted key group on a CloudFront distribution, and CloudFront checks it at the edge before serving the file from cache or the S3 origin. Because no IAM session is involved, it can be valid for much longer. A custom policy can also set a start time, restrict the link to an IP range and use a wildcard to cover many files with one signature. Use S3 presigned URLs for one-off transfers and uploads; use CloudFront signed URLs when you already serve the content through CloudFront or need longer-lived or IP-restricted links.
When a presigned URL is the wrong answer
Presigned URLs are an excellent mechanism and a poor process. They give you an expiry and nothing else: no list of outstanding links, no way to revoke one, no recipient identity, and an audit trail that records the signing principal rather than the person who opened the file.
That is fine system to system, fine for a one-off download, and fine for accepting an upload from a form. It is not a client-facing sharing workflow. If the requirement is "the recipient verifies who they are, the link can be withdrawn, and we can see every open", the primitive to build on is a share with an identity attached, not a signature with a timer. That is the model the BucketDesk S3 workspace uses for client sharing.
The four ways to reach S3 files without the consoleWhat a share needs before it leaves the company
Primary sources
- AWS: Download and upload objects with presigned URLs ↗
- AWS: Sharing objects with presigned URLs ↗
- AWS: Uploading objects with presigned URLs ↗
- AWS: Authenticating requests with query parameters (SigV4) ↗
- AWS: Signature Version 4 policy keys for S3 ↗
- AWS Prescriptive Guidance: Overview of presigned URLs ↗
- AWS Prescriptive Guidance: Presigned URL guardrails ↗
- AWS CLI: aws s3 presign ↗
- Boto3: generate_presigned_post ↗
- AWS SDK for JavaScript v3: @aws-sdk/s3-request-presigner ↗
- AWS: CloudFront signed URLs ↗
- AWS: Checking object integrity in Amazon S3 ↗
Discussion
0 comments · open to guests · moderatedLiked this? Get the next article by email. No schedule, no digest, one click to leave.